
Part-IS, the European Union Aviation Safety Agency (EASA) framework for managing information security risks that could affect aviation safety, became applicable to certain aviation organizations on 16 October 2025. Part-21 design and production organizations, aerodrome operators, and apron management service providers must comply. Created in response to information security threats, the regulation firmly embeds cybersecurity and information security within aviation safety.
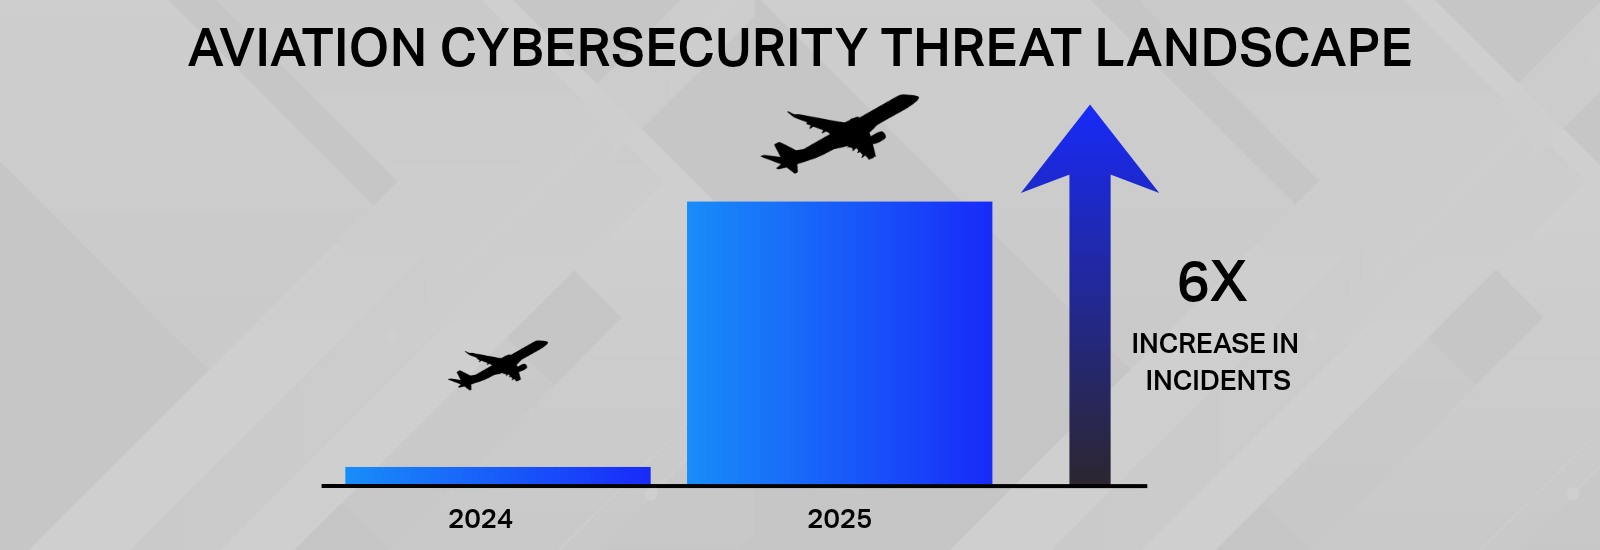
Part-IS is not a general cybersecurity framework like the European Union’s NIS2 Directive. It is an aviation safety regulation that treats information security as a potential safety risk. Its focus is not simply whether a system is technically secure, but where and how information security risks could affect aviation safety.
Put simply, if an organization’s information is compromised, altered, falsified, disclosed, or becomes unavailable, what operational or maintenance safety risks could follow?
Four areas of note to consider include:
Part-IS also extends beyond information stored in IT or operational technology (OT) systems. It applies to information regardless of format, including operational documentation, maintenance records, procedures, and manuals, whether stored electronically or in physical form. The focus is not the technology itself, but the potential impact that the loss of confidentiality, integrity, authenticity, or availability of information could have on aviation safety.
"Consider a cyberattack on maintenance records in which information is stolen or altered. There is an obvious technology element, but what information was at risk? Was it critical to operations and safety? Who needs to know, what could be done with the information, and what does it mean for an aircraft’s airworthiness? These questions require expertise from across information security, safety, operational, engineering, and airworthiness disciplines."
-Mariusz Pyzynski, IATA’s Manager Aviation Information Security
Part-IS requires aviation organizations to implement an Information Security Management System (ISMS). This is a structured set of policies, procedures, governance arrangements, and technical controls for managing information security risks that may affect aviation safety. It goes beyond firewalls and antivirus software by creating an organization-wide approach to managing information security risks that could affect aviation safety.
Key ISMS components include:
Most ISMS frameworks draw on international standards, such as ISO/IEC 27001, which are widely recognised across industries and align with aviation’s safety culture. However, ISO/IEC 27001 certification alone does not constitute compliance with Part-IS.
Aviation safety has traditionally focused on physical risks, such as aircraft performance, human factors, and operational procedures. Today, information security vulnerabilities, whether digital or non-digital, can also affect safety. For example, a cyberattack on flight planning software could cause operational disruption or, depending on the nature and severity of the compromise, potential safety consequences.
An ISMS helps organizations manage information security risks affecting systems and information used for functions such as maintenance and crew scheduling, while supporting operational resilience and continuity. Although designed to support aviation safety, an ISMS may also help organizations meet broader information governance and regulatory obligations and maintain public trust.
"Collaboration across teams is essential because no single person holds all the necessary knowledge. Multi-disciplinary teams must work together. Domain experts remain vital, but they also need an awareness of the wider safety picture, because information security risks must be evaluated not only for their technical impact but also for their potential consequences on aviation safety. "
-Mariusz Pyzynski, IATA’s Manager Aviation Information Security
Airlines already have mature Safety Management Systems (SMS) and Security Management Systems (SeMS), which have been required for many years, and Part-IS is structurally modelled on the SMS framework.
However, Part-IS establishes specific requirements for managing information security risks that may affect aviation safety. Organizations should not assume that an SMS satisfies all Part-IS requirements, nor simply transfer information security risks into an existing SMS risk register. These risks need dedicated processes, governance, and oversight. Where appropriate, organizations should integrate the ISMS with existing management and safety systems, while keeping Part-IS requirements clearly documented and auditable.
Nevertheless, an SMS can provide a bridge to an ISMS by helping cyber and safety specialists work together. An ISMS also helps organizations manage information security risks arising from external interfaces and dependencies, including relationships with suppliers and other aviation organizations.
In addition to an ISMS, Part-IS requires an Accountable Manager with the authority and responsibility to ensure that all information security activities meet applicable requirements.
The Accountable Manager is responsible for ensuring that appropriate resources, responsibilities, and governance arrangements are in place. The organization must ensure that sufficient competence exists in both information security and aviation safety to support compliance with Part-IS.
Organizations also need ISMS documentation, typically maintained within an Information Security Management Manual, as part of their compliance framework.
Finally, the ISMS must include a continuous improvement process. It is not a one-off project, but a lasting organizational culture shift.
Successful Part-IS implementation depends not only on information security expertise and organizational coordination but also on building the right competencies, awareness, and culture across the organization.
Part-IS requires both organizational and technical measures and represents a broader cultural shift. It provides a systematic way to manage information security risks and protect critical assets. Everyone in the organization, from information security experts and engineers to operational personnel and flight crews, has a role in maintaining information security.
This involves recognizing and reporting suspicious activity and using secure passwords and devices. Just as safety is embedded in aviation operations, information security awareness must become second nature.
In general, aviation organizations already have many of the competencies needed to comply with Part-IS. Even so, leadership involvement is essential because Part-IS requires responsibility and accountability across the organization. Communication should position the regulation as part of the organization’s wider safety efforts, and all roles must understand the requirements and have the right knowledge and expertise.
Just Culture principles are equally important. Employees must feel able to report information security issues in an environment that encourages reporting and learning while maintaining appropriate accountability.
"Part-IS affects everyone because any person may interact with information that is important to safety. Whether information is disclosed, altered, falsified, or becomes unavailable, even a seemingly minor issue can trigger a chain of events that leads to significant safety consequences."
-Mariusz Pyzynski, IATA’s Manager Aviation Information Security
Emphasizing information security as an aspect of safety requires training. Information security specialists, safety specialists, operational personnel, engineers, quality professionals, and managers may require further training to strengthen their understanding of information security risks, their potential impact on aviation safety, and their respective roles in managing those risks. And greater awareness needs to be integrated into the company culture.
IATA - Aviation Cybersecurity and Part-IS Fundamentals: A practical introduction to aviation cybersecurity, with dedicated coverage of EASA Part-IS. Participants learn how cyber incidents can affect aviation safety, security, and operations, helping them strengthen resilience and apply robust information security practices across aviation environments.
Other practical resources to strengthen your Part-IS readiness


